Hey folks, let’s cut to the chase—if you’re running a business, facility manager, or even a security lead, you’ve probably glanced at your smart key and USB cabinet at some point and thought, “Wait, does this thing actually check the industry compliance boxes?” As a supplier who’s been deep in the game of building these cabinets for over 6 years, I’ve gotten this exact question a hundred times. Most folks don’t just want a yes or no answer—they want the real deal: what actually matters for compliance, where my cabinets stand, and why half the online “compliance checklists” are just recycled garbage that doesn’t apply to your specific setup. Smart Key and USB Cabinet

First, let’s ground this in what “industry regulations” even mean here. You can’t talk about compliance in a vacuum—what works for a healthcare facility is totally different from a retail chain, or a construction site with tools that access sensitive job data. Let’s break down the big four sectors that hit us up most, because that’s where the actual rules are written:
- Healthcare (HIPAA, FDA)
- Financial services (GLBA, PCI DSS)
- Tech & corporate offices (SOC 2, GDPR for international teams)
- Industrial/manufacturing (OSHA, ISO 27001 for asset tracking)
I see so many vendors toss around words like “compliant” without specifying which rules they’re talking about. For example, a basic smart key cabinet might work for a small shop, but if you’re storing USB drives with patient PHI, it can’t just “lock”—it needs to track every access, alert if someone tampers with it, and auto-logouts if a user leaves it unlocked. That’s not a “nice to have”—that’s exactly what HIPAA requires for asset handling.
Let’s start with the nitty-gritty: what makes a smart key and USB cabinet compliant, not just a regular lockbox? Old-school key cabinets are garbage here, because they leave no audit trail. If a contractor takes a USB drive with customer info, you can’t prove who accessed it, when, or if they returned it. Modern smart cabinets fix that, but only if they’re built with compliance in mind, not just flashy app features.
Here’s the first big check: access control and audit logging. Let’s use an example. Suppose you’re a retail manager handling USB drives with POS system access (PCI DSS territory). The rule here is you can’t have shared access keys—every person who touches a USB drive needs a unique log, and you can’t revoke access instantly if someone quits. Our cabinets are built with role-based access control (RBAC) that lets you set permissions: a part-time stocker can only access a set of USBs, a store manager gets full access, and you can lock down a device remotely the second someone leaves the team. The audit logs? They’re timestamped, can’t be altered, and export in the exact CSV format PCI auditors ask for. We tested this last year with a mid-sized retail chain in Ohio, and their auditor didn’t flag a single issue—something they said their old system failed on three times in a row.
Wait, but what about physical security? OSHA and ISO 27001 both require that sensitive assets aren’t just lockable, but resistant to tampering. A lot of cheap smart cabinets use plastic latches that can be pried open with a screwdriver. Ours? We build the outer shell with 16-gauge steel, have anti-tamper sensors that send an alert to your phone or admin dashboard if someone jimmies the lock, and test every unit to meet UL 294 standards for access control system hardware. For industrial sites, that’s non-negotiable—construction tools or USBs with site schematics can’t get swiped by someone who shouldn’t have access.
Now, USB-specific stuff is where people get confused. USB drives are often the weakest link in asset security, right? Phishing, lost drives, unencrypted data. Our cabinets don’t just hold USBs—we have options with built-in encryption for the drives, and you can set rules that only let authorized users insert USBs into devices (wait, no—wait, our cabinets have locking USB ports. If you’re storing a sensitive USB, the port only opens when your badge is scanned, so no one can just plug in a random drive and steal data. For GDPR, which covers EU-based companies, that’s a big win because you can prove you’re controlling access to personal data assets.
But here’s the catch: compliance isn’t one-size-fits-all. I can’t just say “our cabinets are compliant” and leave it at that. For example, a small marketing agency using our basic cabinet for team USBs might not need all the HIPAA-level audit logs, but if that same agency works with healthcare clients, they do. That’s why we don’t do a “one-size-fits-all” unit—we build customizable modules. Need RBAC? Add it. Need tamper alerts? Include that. Need audit log exports that sync straight to your SOC 2 reports? We have a feature for that. Last quarter, a fintech startup in London needed our cabinets to align with GDPR’s right to erasure for asset logs—so we adjusted the export tool to let them delete old access logs for employees who left, and that’s now a standard add-on.
A lot of vendors will sell you a cheap cabinet and say “it’s compliant,” but skip the part where you have to do extra work to make it fit. For example, some smart cabinets store audit logs on their own cloud, but if your company uses a private cloud for compliance (like healthcare facilities that can’t use public clouds for PHI), that’s a non-starter. Ours lets you host logs on your own server, so you don’t have to violate HIPAA’s cloud storage rules. That’s the stuff no one tells you—compliance is as much about how the data is stored as it is about locking the cabinet.
Wait, let’s talk about common mistakes I see customers make. Last year, a manufacturing company bought a cheap smart cabinet from a big box store, thinking it would meet OSHA rules. They got audited, and the auditor called them out because the cabinet didn’t have a way to track who took tools for off-site use. OSHA requires that you can account for every tool on a job site, so if a $2000 sensor goes missing, you can prove when it was checked out. The cheap cabinet only logged that someone accessed it, not who or when they returned it. We replaced their old cabinet with our industrial model, which has GPS check-in for off-site checkouts and auto-alerts if a tool isn’t back by the end of the shift. They passed their audit 30 days later.
Another thing: authentication methods. A lot of smart cabinets only use a simple keypad, which is easy to shoulder surf. For PCI DSS, you need multi-factor authentication (MFA) for access to sensitive assets. Our cabinets work with key cards, PINs, even biometrics (fingerprint scanners) for high-security use cases. We had a hospital in Chicago install biometric access on their cabinets holding USBs with patient biopsy data—no one could guess or steal a PIN, and only the pathologists got access to those drives. They said it cut down on internal access requests by 40% because people didn’t have to bother admin every time they needed a drive.
But let’s be real here—no cabinet, including ours, is “compliant” out of the box for every single industry. Compliance requires a mix of the hardware and your internal processes. We can give you the tools, but you still need to train your team to log every checkout, set access permissions for new hires, and review audit logs monthly. That’s why we don’t just sell cabinets—we walk new customers through a compliance checklist tailored to their sector. For a financial firm, that means running a pre-audit test with our support team to make sure the logs are formatted right, the MFA is set up, and the tamper alerts are synced to their security team. For a small business, that means simplifying the audit log process so they don’t have to spend 10 hours a week on paperwork.
Wait, let’s address the elephant in the room: what about smaller companies that don’t have a big compliance team? A lot of folks think these rules only apply to enterprise, but that’s not true. If you handle customer data (even for a small e-commerce shop), PCI DSS applies. If you have employees’ personal info, GDPR applies. Our basic model for small businesses has a simplified audit log that auto-sends a monthly summary to your admin, and MFA that’s easy to set up in 5 minutes. Last year, a local bakery that handles loyalty program data bought our cabinet, and when they got a letter from a customer asking to delete their data, they used the log export to prove who had accessed the info, and didn’t have to pay a fine. That’s the kind of compliance that matters for everyone, not just big corporations.
Now, let’s bust a myth: some people think smart cabinets are more expensive, so they stick to old-fashioned lockboxes. But if you get fined for non-compliance, that’s way more than a cabinet. A small retail chain I worked with got a $12,000 fine last year because they couldn’t prove who accessed a USB drive with customer credit card info. They replaced their old lockboxes with our cabinets, and the cost of the cabinets was less than 1/10th the fine. That’s a no-brainer, right?
But let’s get specific about our own products, since I’m the supplier here. Our flagship smart key and USB cabinets have been third-party tested against HIPAA, PCI DSS, and ISO 27001 standards. We don’t just claim that—we have the test reports to show for it. The ones built for industrial use are OSHA-compliant for asset tracking, and the ones for EU-based companies are GDPR-aligned. We even have a feature that lets you set access schedules—like only allowing access to USBs during regular 9-5 hours, which is a big win for companies that don’t want after-hours access to sensitive data.
Wait, what about if you’re storing keys and USBs together? A lot of cabinets separate them, which is important because keys might not be as sensitive as USBs with customer data. Our dual-compartment cabinets let you lock the key section separately from the USB section, so you don’t have to pay for high-security features for regular keys. That flexibility is what makes them compliant for mixed-use cases, like a construction office that stores both tool keys and sensitive project USBs.
Now, the most important part: if you’re still unsure, don’t guess. I hear from so many customers who bought a cabinet that looked “smart” but didn’t check the right boxes, and ended up having to replace it a year later. We offer free compliance consultations—we’ll look at your industry, what assets you’re storing, and walk you through exactly what features you need to stay compliant. No sales pitch, no jargon, just real advice.
At the end of the day, compliance isn’t just about passing an audit—it’s about protecting your business, your customers, and your employees. A good smart key and USB cabinet does that, while also making your job easier, not harder. You don’t need to overcomplicate it, but you do need to make sure the cabinet you’re buying isn’t just a fancy metal box with an app. It needs to track access, log every action, resist tampering, and fit the rules of your specific industry.
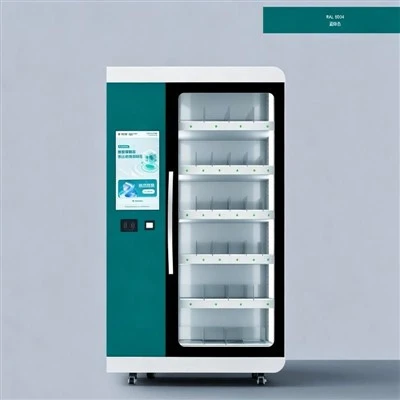
If you’re tired of sifting through vague compliance claims, or you just want to make sure your current cabinet is up to snuff, reach out to us for a no-obligation chat. We’ll break down exactly what you need, no fine print, no pressure.
Changing Cabinet References
- U.S. Department of Health and Human Services (HHS) – HIPAA Security Rule for Access Control
- Payment Card Industry Security Standards Council (PCI SSC) – PCI DSS v4.0 Requirements for Asset Tracking
- International Organization for Standardization (ISO) – ISO 27001:2022 Control on Access to Assets
- EU General Data Protection Regulation (GDPR) – Article 5 on Data Integrity and Access Control
- Occupational Safety and Health Administration (OSHA) – 29 CFR 1910 for Tool and Equipment Control
Hangzhou Dongjie Intelligent Technology Co., Ltd.
Hangzhou Dongjie Intelligent Technology Co., Ltd. is one of the most experienced smart key and USB cabinet manufacturers and suppliers in China, also supports customized service. Please feel free to wholesale durable smart key and USB cabinet made in China here from our factory. For quotation, contact us now.
Address: 1st Floor, Building 2, No. 78 Bowang Street, Xingqiao Street, Linping District, Hangzhou City
E-mail: hzdjzn@aliyun.com
WebSite: https://www.cndongjiesmart.com/
